Training · CC Ready series · Published · Last reviewed · By the Red Flag Cyber research desk
CC Ready — ISC2 CC Exam Prep
CC Ready is Red Flag Cyber's ISC2 CC exam-prep series. The pilot covers Domain 1, Security Principles — the CIA triad, threat, vulnerability and risk, and the three control categories — ten original Domain 1 practice questions with explained answers, and a lesson separating the incident response plan, the business continuity plan, and the disaster recovery plan. Practice questions are original to this series; they are not exam questions.
Episodes
A1
ISC2 CC Domain 1: Security Principles — The CIA Triad, Explained
Domain 1, Security Principles, is an average of 24% of the ISC2 CC exam — the biggest single domain. This lesson teaches the CIA triad (confidentiality, integrity, availability) the way the exam tests it: by the harm in a short scenario, not the tool in the story. It also covers threat, vulnerability, and risk, sorts the outline's three control categories (Technical, Administrative, Physical) live on screen, and ends with two original practice questions with explained answers.
10 ISC2 CC Practice Questions: Security Principles — With Explanations
Ten original practice questions on ISC2 CC Domain 1, Security Principles — pause before each answer, say your answer out loud, and keep score. Every question is followed by its answer and a short, source-cited explanation.
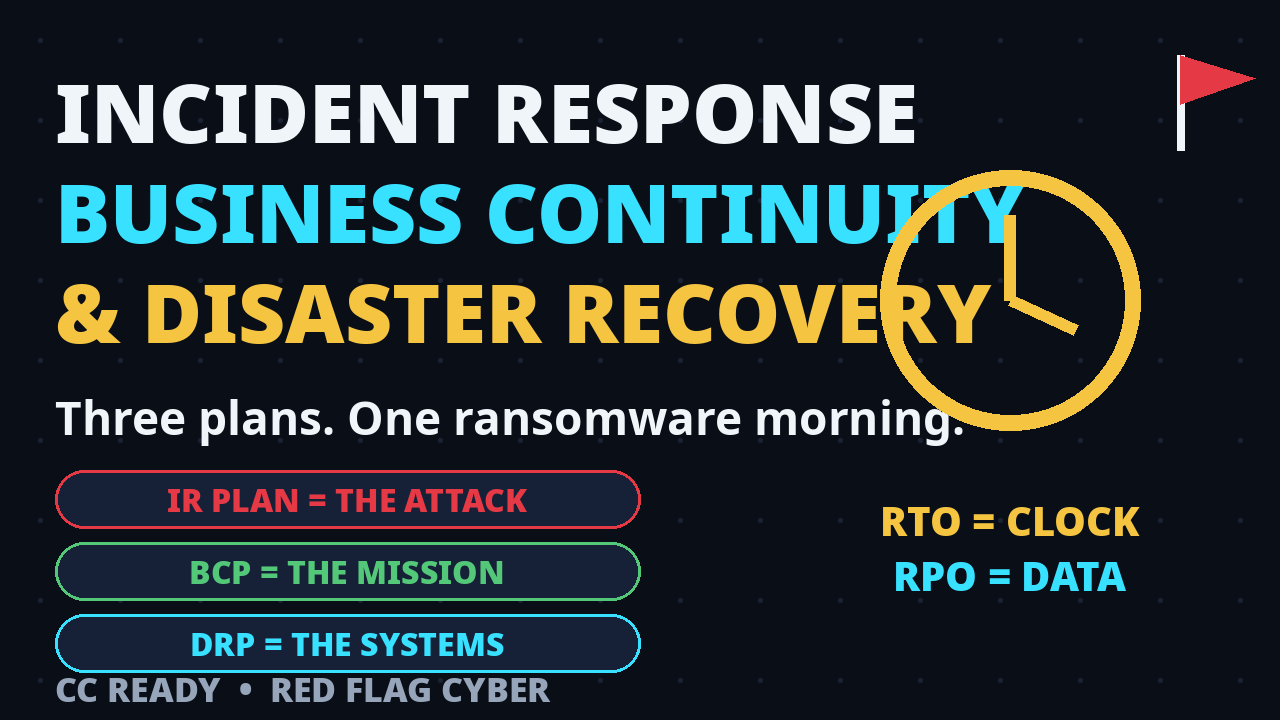
Incident Response, Business Continuity & Disaster Recovery
A ransomware morning, three different plans. This CC Ready lesson separates the cyber incident response plan (the attack), the business continuity plan (the mission), and the disaster recovery plan (the systems) — and maps each one to where it actually sits on the current ISC2 CC outline: business continuity and disaster recovery under Domain 2 §2.2 (redundancy), incident response under Domain 5 §5.3. Covers the NIST SP 800-61 Rev. 3 incident response model (and the withdrawn Rev. 2 four-phase model, labeled as previous), full / incremental / differential backups, RTO vs RPO and the business impact analysis, alternate sites, and tabletop exercises — plus two original practice questions with explained answers.